On October 21, 2026, Node.js shipped security releases across all supported lines fixing a high-severity out-of-bounds write in the bundled Brotli decoder. A Node.js process that decompresses attacker-controlled Brotli data — including Brotli-encoded HTTP responses it fetches — can be driven to write past the end of its buffer, leaking memory or executing code with the process’s privileges.
What is Node.js?
Node.js is a widely used server-side JavaScript runtime that powers a large share of web backends, APIs, build tooling and serverless functions. It bundles Google’s Brotli library (`deps/brotli`) to back its built-in `zlib` Brotli support — `zlib.brotliDecompress()` / `brotliDecompressSync()`, streaming Brotli, and the transparent decoding of Brotli-encoded HTTP bodies (`Content-Encoding: br`).
Because decompressing untrusted Brotli is common (fetched HTTP responses, uploaded or proxied payloads), a decoder memory-safety bug is reachable from ordinary traffic across a huge range of services, and a WAF does not mitigate it.
Affected versions
| Package | CVE | Component | Versions | Fixed Versions | Ecosystem | CVSS v4.0 |
| node | CVE-2026-111497 | Brotli decoder (bundled `deps/brotli`) | < 22.23.4, < 24.22.1, < 26.12.1 | 22.23.4, 24.22.1, 26.12.1 | Node.js runtime | High (no CVSS) |
CVE-2026-111497 – Brotli decoder out-of-bounds write -> RCE
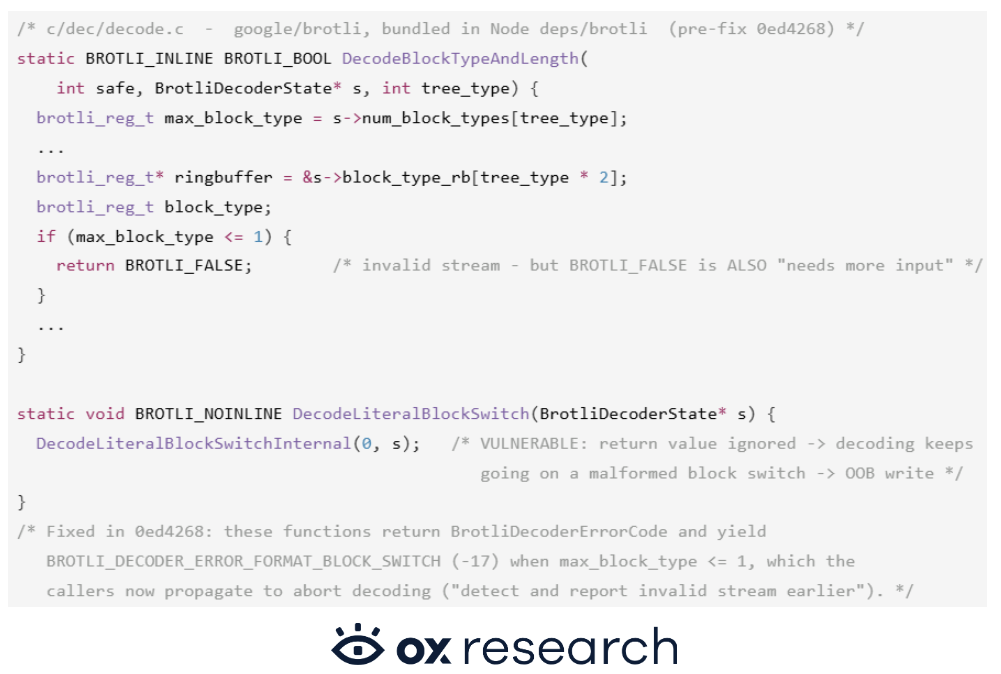
Brotli can split literals, commands and distances into block types and switch between them mid-stream. `DecodeBlockTypeAndLength` returned a `BROTLI_BOOL`, overloading `BROTLI_FALSE` to mean both “invalid stream” (only one block type, so a block switch is illegal) and “needs more input.”
The block-switch callers treated that `BROTLI_FALSE` as recoverable – and `DecodeLiteralBlockSwitch` discarded the result entirely – so a malformed block switch did not stop decoding: the decoder continued with invalid state and wrote out of bounds.
Recommendations
- Upgrade now. Node.js 22.23.4 / 24.22.1 / 26.12.1. End-of-life lines (25.x, 23.x, <= 20.x) get no fix – move to a supported line.
- Treat Brotli decompression of untrusted input as the sensitive path. Anything that calls `zlib.brotliDecompress(Sync)` on attacker data, or fetches Brotli-encoded responses (sends `Accept-Encoding: br`), including indirectly through libraries.
- Be wary of PoCs and “patch” scripts. Do not clone or run unverified exploit or patch scripts from public repos or social media; trust the Node.js advisory and the official releases.