


OX VibeSec
AI usage security for every user, agent and tool. Prevention you can prove.

Trusted by hundreds of enterprises around the world


In the era of ungoverned agents, MCPs, and skills, OX VibeSec governs every AI user and AI-driven process in your organization, embedding visibility and control directly into workflows.


Prevention at the Prompt
Secure AI code as it’s written and stop secrets in prompts before they reach a model.
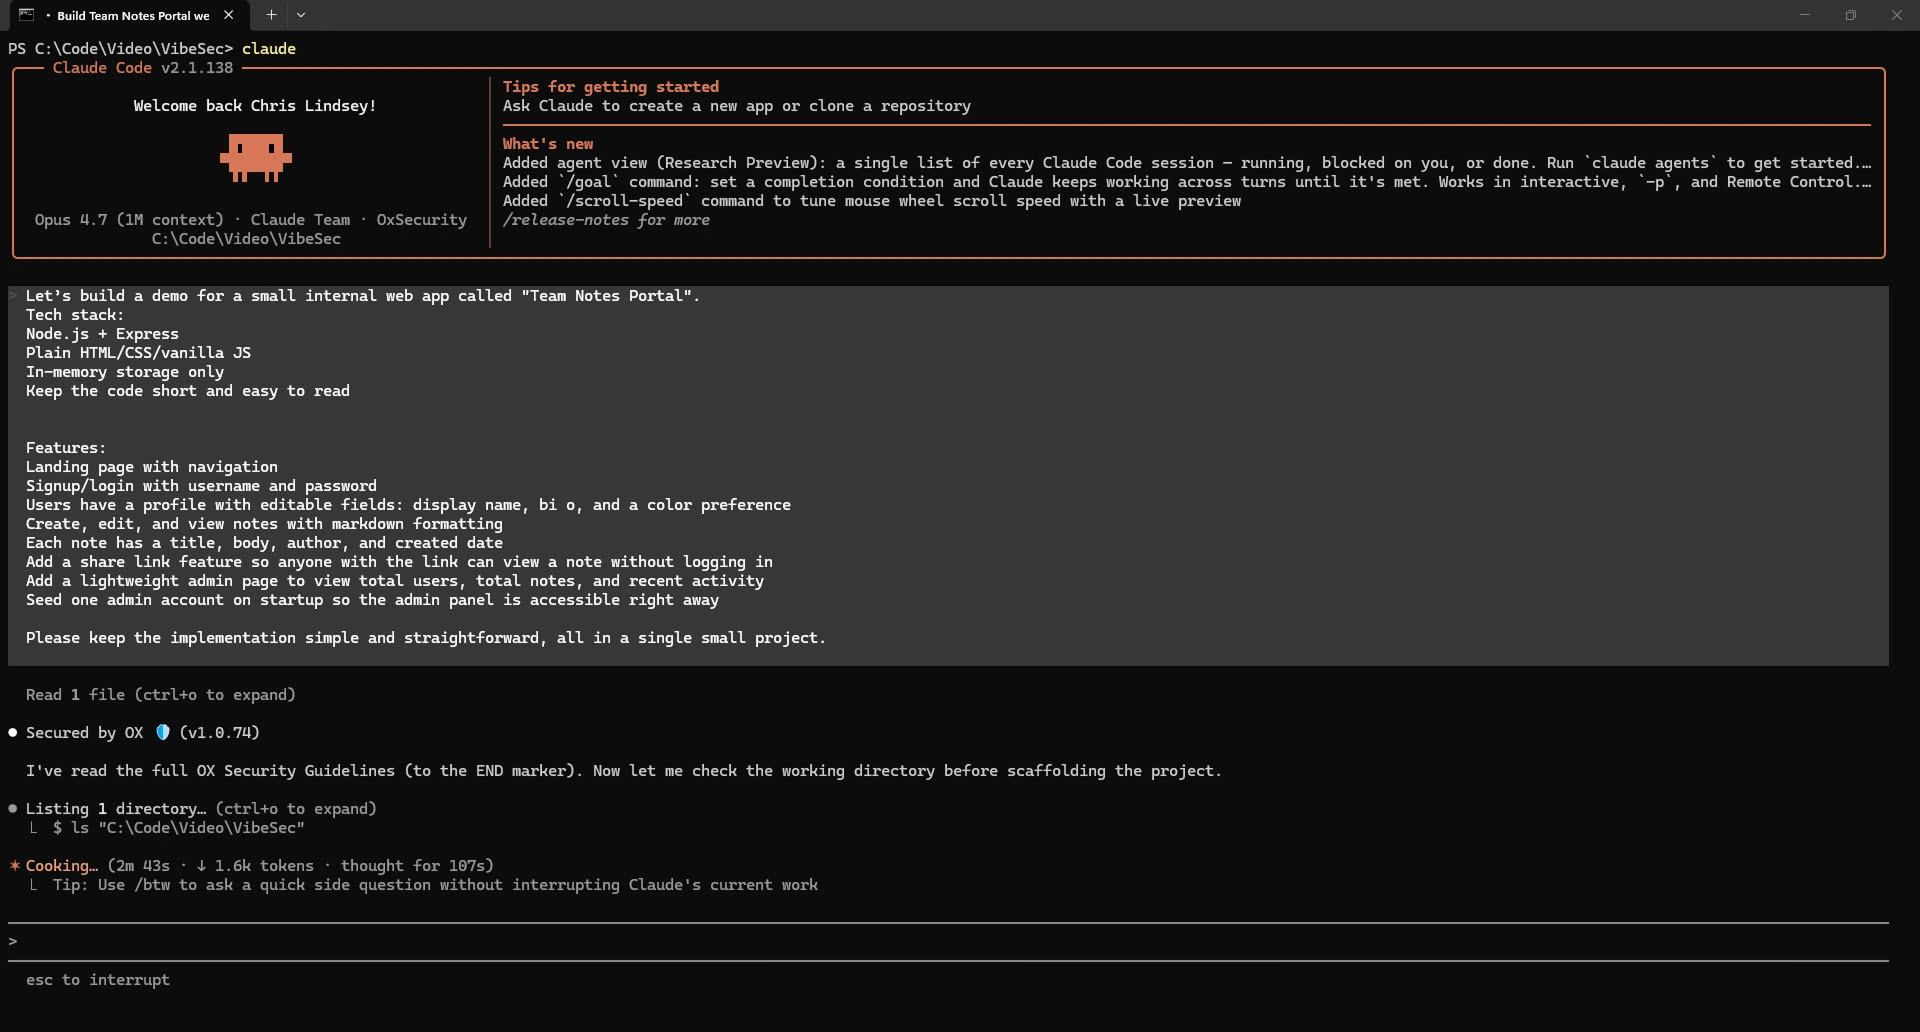


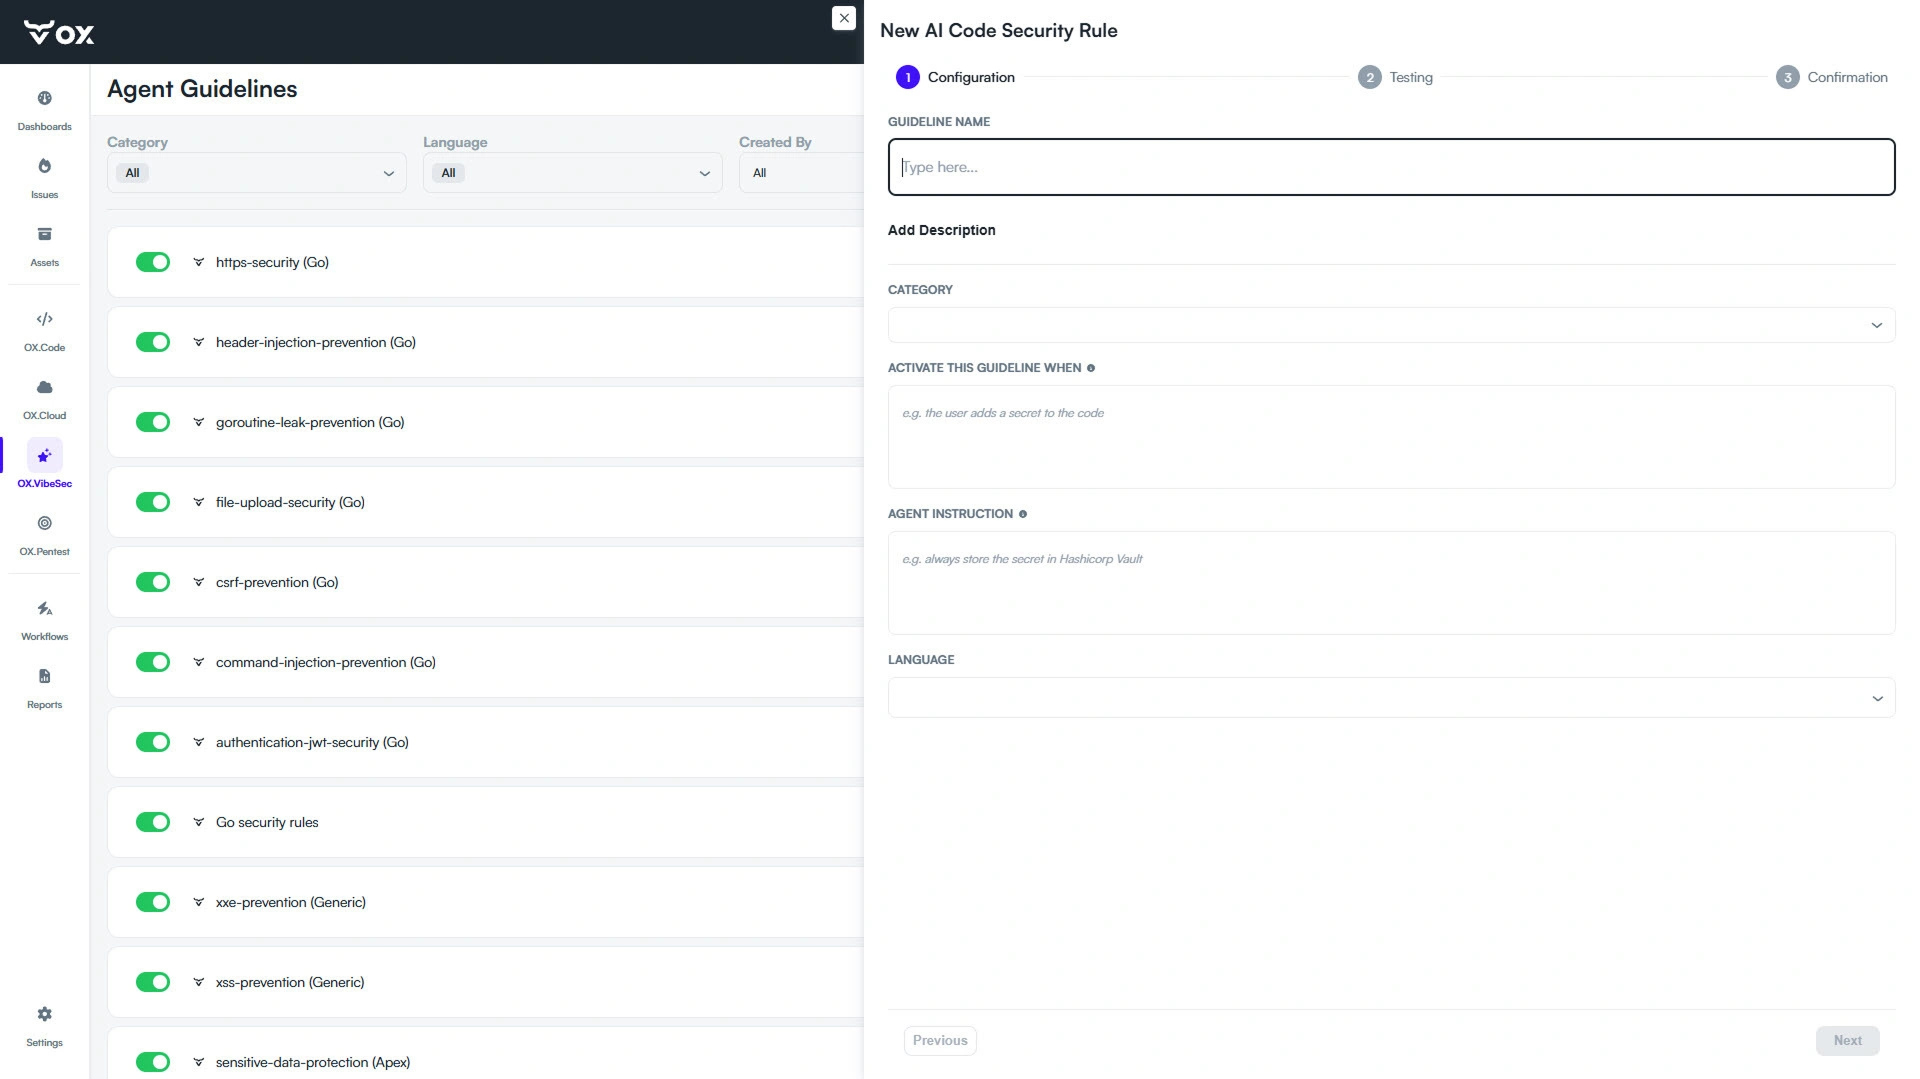


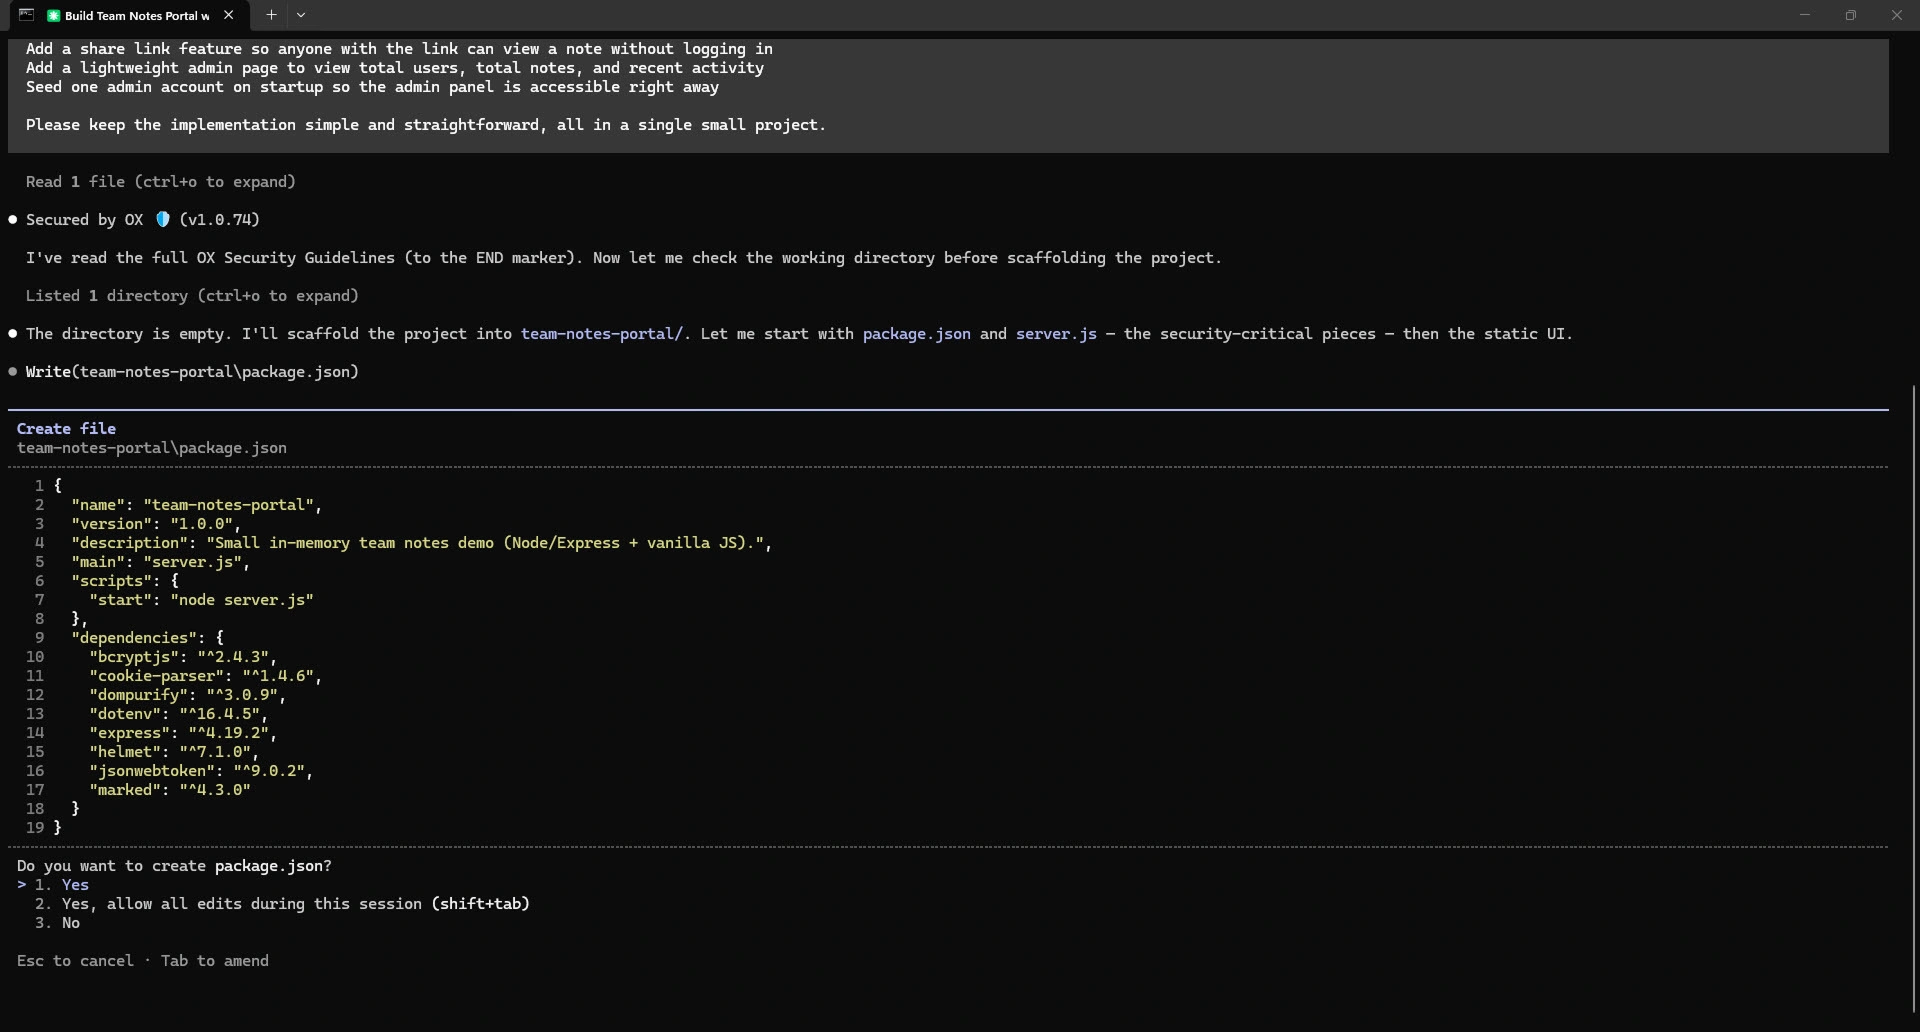
Guidelines make AI-written code secure. VibeSec classifies each prompt and serves the agent the right security guideline as the code is written. Every dependency an agent adds is checked, malicious packages are blocked before they land, and secrets are stopped inside the prompt.
Test your
environment today
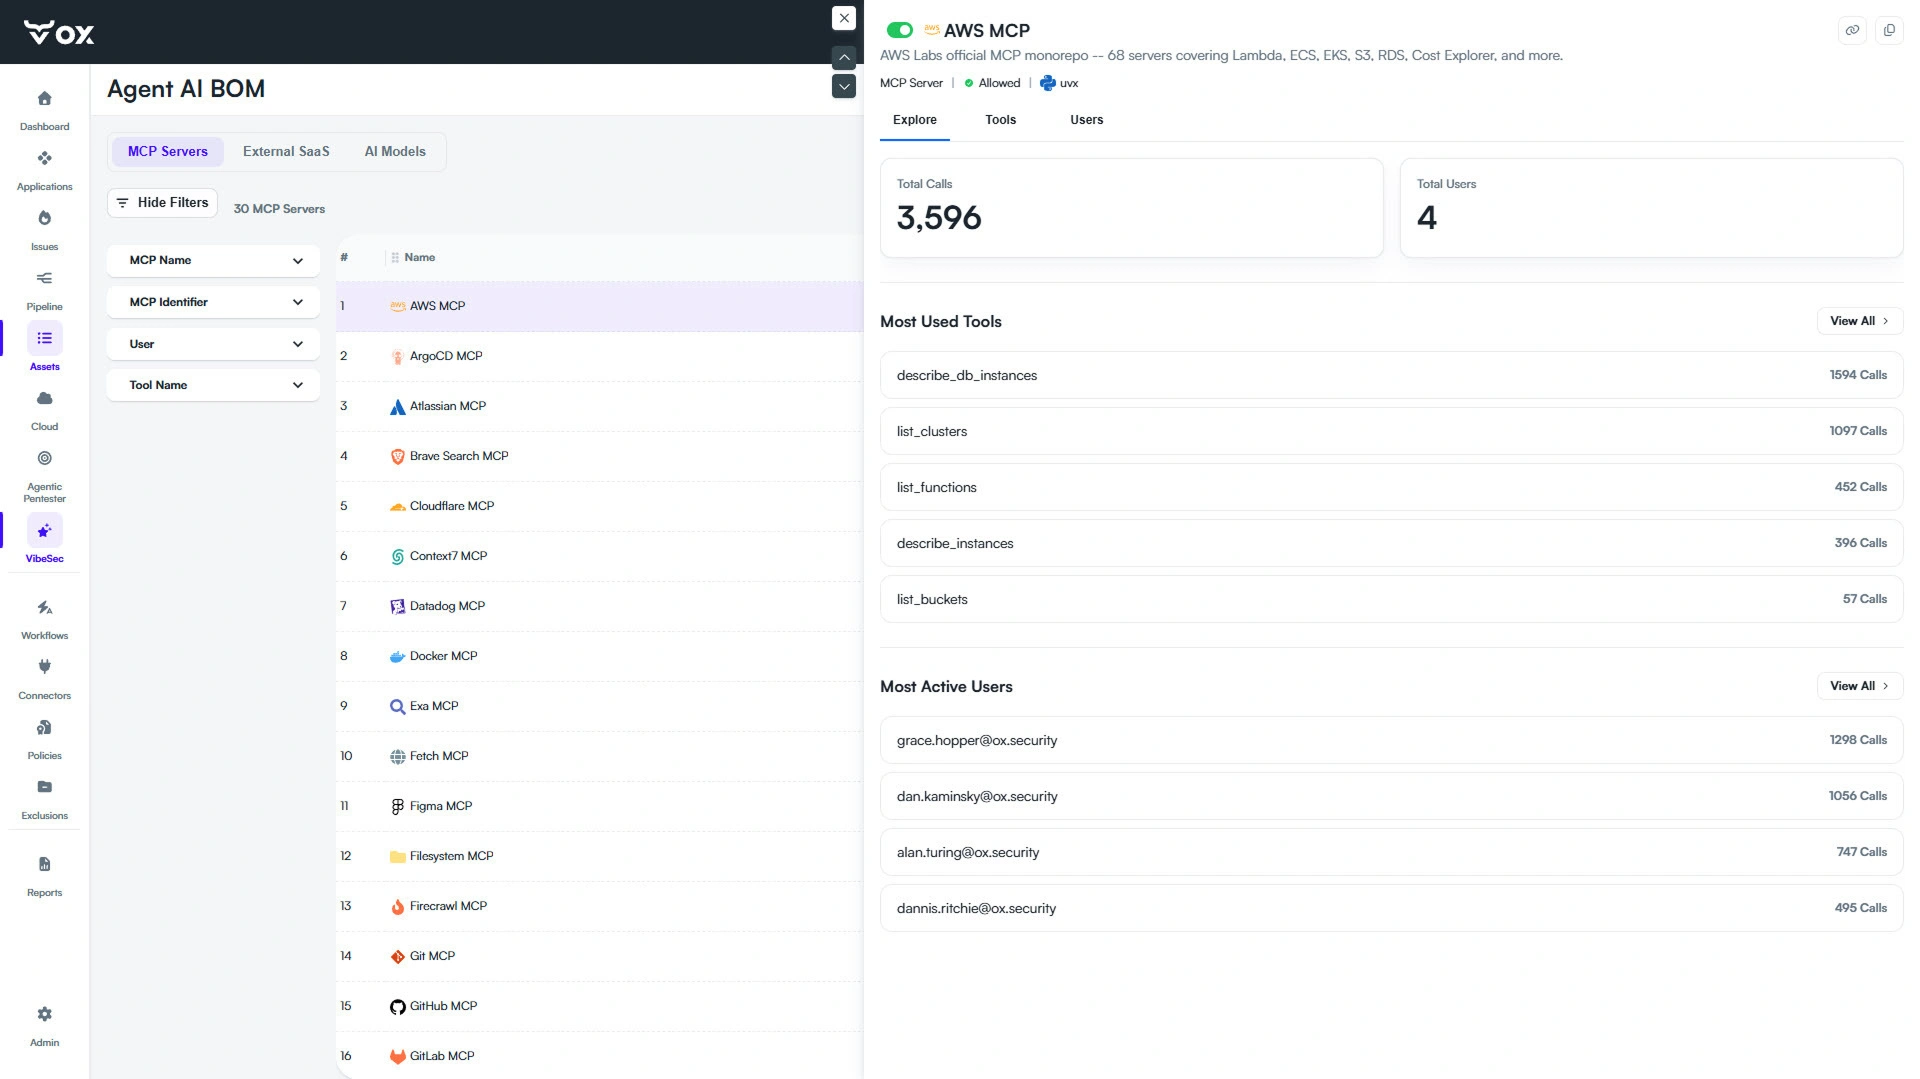
See every AI tool, and why it’s risky. VibeSec identifies every MCP server, skill, model, external SaaS tool and AI user, and inspects skills for malicious instructions and hidden behavior. Each one gets a verdict and the reasoning behind it, so teams know exactly what to block.

Analysis backed by industry leading
threat and vulnerability research


Guardrails for every agent action as it happens. Policies evaluate what agents do at the point of action, across prompts and tool calls, then allow, flag or block. That covers risky behavior like destructive actions and data leakage, and attacks like prompt injection and agent hijacking.

The developer sees a moment. Security sees the record. Every flag or block opens an OX issue tied to the application it would have hit and its criticality, in the queue AppSec already uses. Start by observing, then enforce with one toggle when the evidence says so.

Stop reacting to AI risk. Start governing it.
