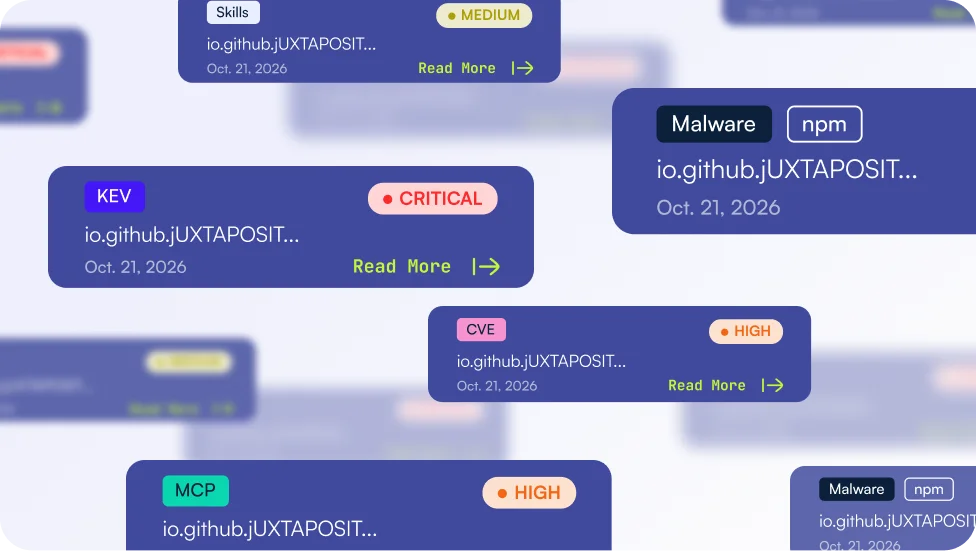
The public OX.Radar site shows what broke. Anyone can search 785K+ tracked assets across the AI stack and software supply chain, from MCP servers and skills to npm and PyPI packages, see risk scores, and read OX Research’s findings on the latest threats.
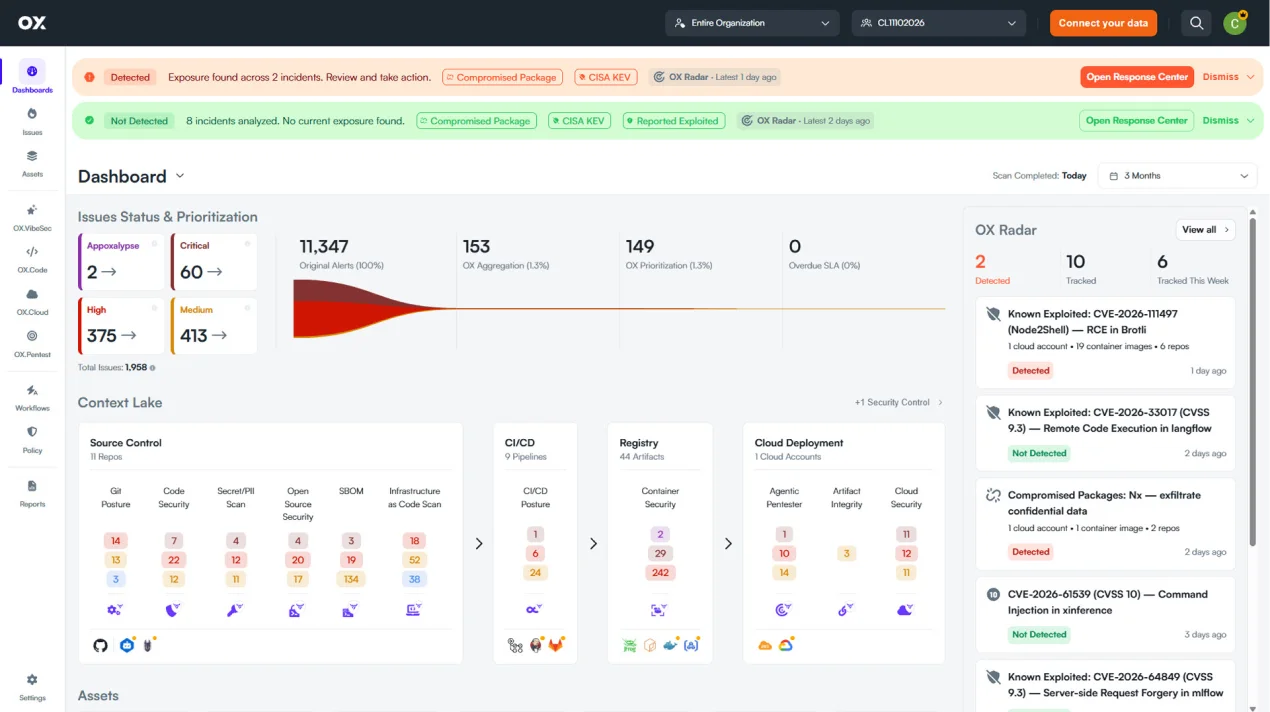
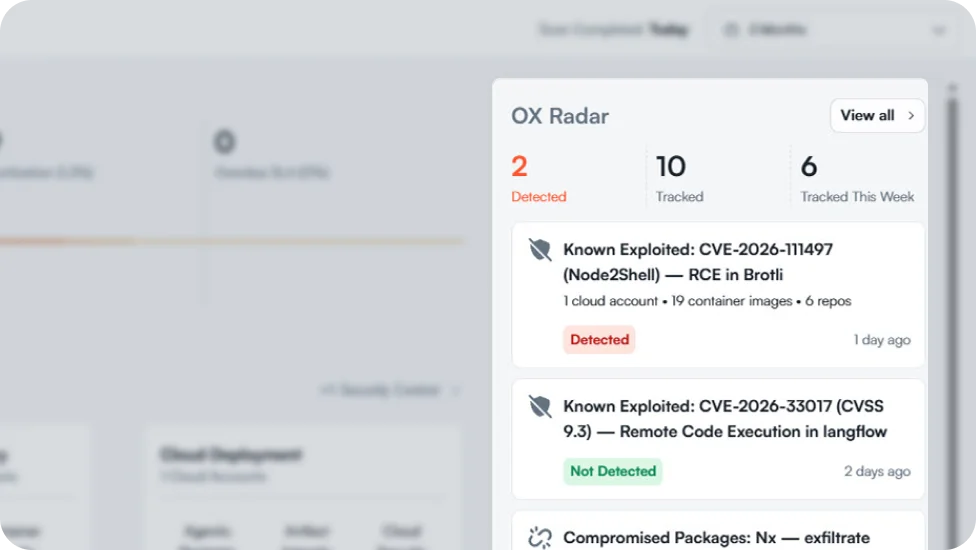
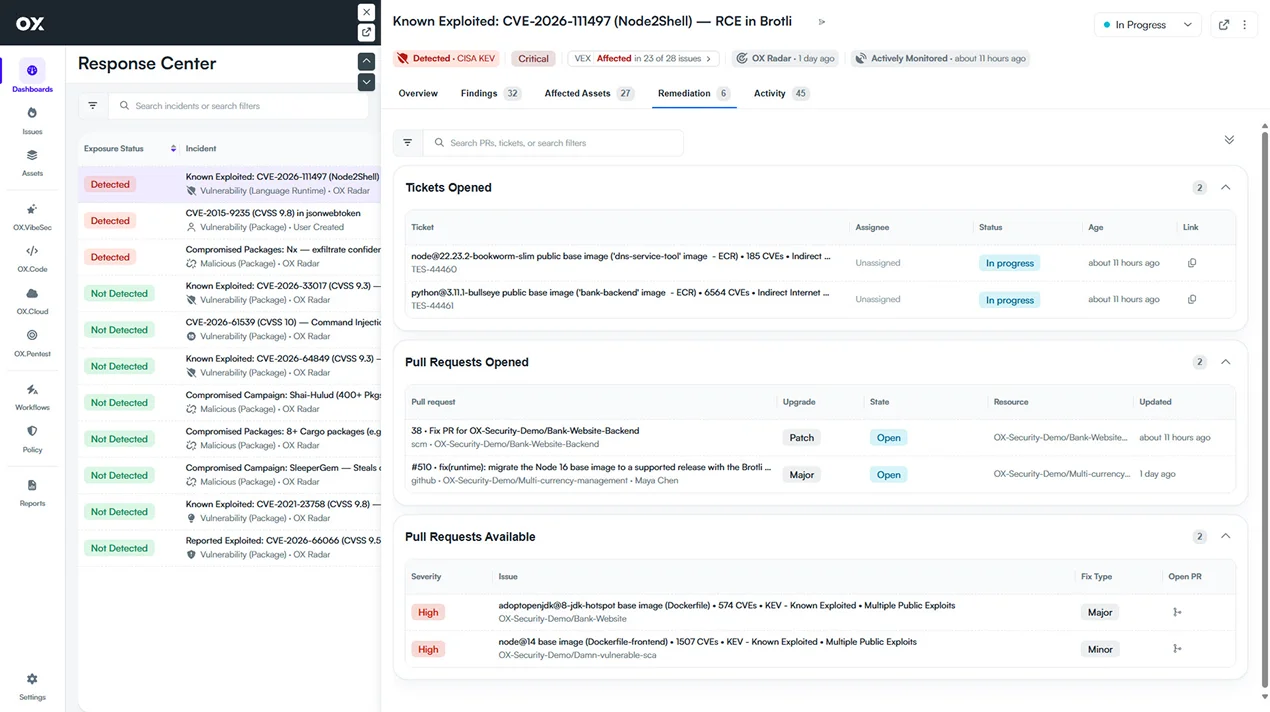
OX Radar in the product shows if an incident broke you. Because OX is one platform with a shared context lake, the Response Center will check the most urgent supply chain threats against customer’s code, cloud and developer environments, including: compromised and malicious dependencies, known exploited vulnerabilities (with real-time CISA and EU KEV integration), new CVSS 10 vulnerabilities, critical vulnerabilities in popular packages, and reported or rumored exploits. When a threat is Detected, you see exactly which assets it touches and how to fix them; when it’s Not Detected, you have evidence ready to share with leadership.