Built for a new class of active, dynamic risk that traditional cloud security wasn’t built to see.
TL;DR
- OX Cloud unifies CNAPP (cloud posture management) with real-time AI and non-human identity detection.
- Combining CNAPP coverage with live AI detection (AIDR) and deep runtime inspection, OX Cloud uses reachability to filter out exposure nothing can actually reach.
- Most CNAPPs rely on periodic scans and generic rules, and AI security point tools add bolted-on inventory alongside them; OX Cloud instead shows what’s actually running, what it’s doing, and whether it matters, in real time.
- As part of the OX AINAPP (AI Native Application Protection Platform), OX Cloud validates that upstream governance holds, rather than only detecting exploitable paths after the fact.
OX Cloud is the runtime pillar of the OX AINAPP platform, and our answer to a question most cloud security tools still aren’t built to ask: what is actually happening in your cloud right now, and does it matter?
Why Most CNAPP Tools Miss AI Agents Running in the Cloud
Cloud security has stopped meaning what it used to mean. It used to be all about things that sat still long enough for a nightly scan to catch them: servers, containers, storage buckets, IAM roles, etc.
Many environments have moved on from all that. Agents call tools. Models access data. MCP servers execute on their own, making decisions no human explicitly authored. None of that shows up cleanly in a posture dashboard built for static infrastructure. This was never designed to watch something that acts on its own.
CNAPPs inventory AI assets; they don’t tie agent runtime behavior to reachability or to the prompt/code that created it. They also weren’t built to watch agents, models and MCP servers acting on their own.
What Is OX Cloud?
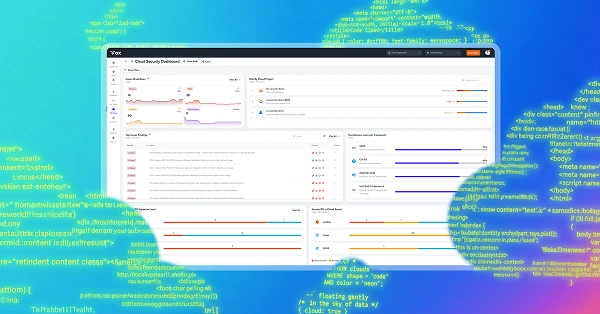
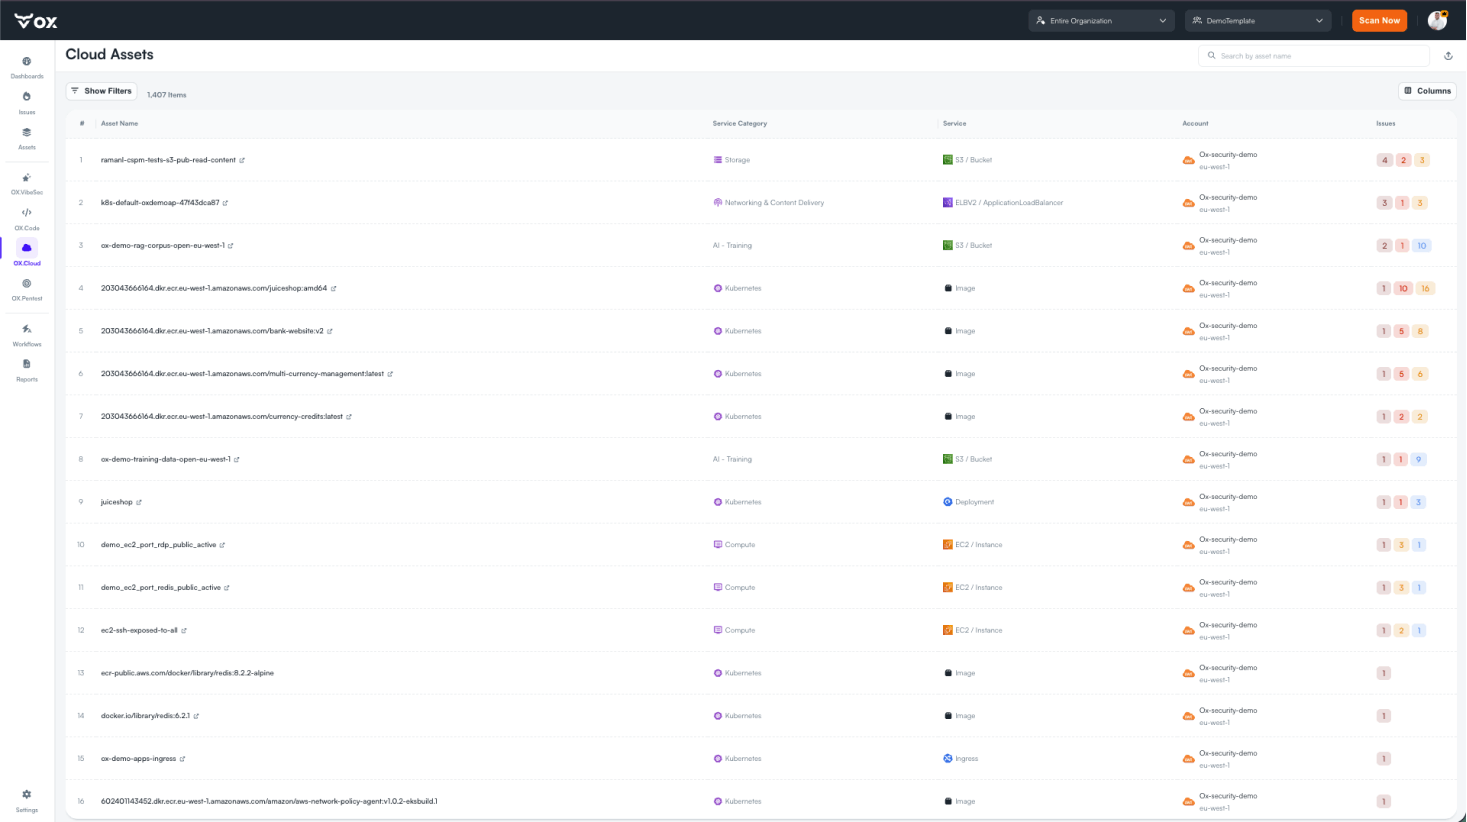
OX Cloud inventories everything actually running in your environment (workloads, identities, data stores, Kubernetes clusters, and AI agents as they run) along with the configurations behind them. But inventory is where most other tools stop.
| Capability | What It Does |
| AIDR | Detects and governs any AI-driven usage, configuration, or threat across your cloud and runtime environments in real time. |
| Agentic Attack Surface (Powered by the OX Agent) | Uncovers hidden backdoors and reachable exposures with agentic-level inspection. |
| Runtime Events (Incident Response) | Investigates runtime anomalies with full context to accelerate detection and triage. |
| Runtime Vulnerabilities | Identifies vulnerabilities actively exposed in running workloads and prioritizes what’s truly exploitable. |
| Cloud Graph and Attack Path Mapping | Visualizes relationships across cloud assets to understand exposures, lateral movement, and blast radius at a glance. |
| CSPM (Cloud Security Posture Management) | Continuously detects cloud misconfigurations and enforces compliance across all cloud accounts. |
| KSPM (Kubernetes Security Posture Management) | Monitors K8s security risks in depth, including misconfigurations and policy compliance. |
| DSPM (Data Security Posture Management) | Discovers, classifies, and protects sensitive data across cloud environments. |
| Cloud Inventory | Maintains a complete, always-current inventory of every asset across the cloud estate. |
OX Cloud beyond inventory by watching what’s actually running, what data is touched, and what permissions are held. Then, reachability does the filtering, so misconfigurations, vulnerable packages, and supply-chain exposure that nothing can reach fall away.
As part of the OX AINAPP, OX Cloud unifies traditional posture management with live AI Detection (AIDR) and deep runtime inspection to secure dynamic cloud risk, autonomous agents, and non-human identities so you can prioritize what matters most.
OX Cloud shifts your security from detecting exploitable paths after the fact to validating they were never created in the first place. That’s the runtime security proof point of the same platform story: one context lake, from prompt to runtime.
Why OX Cloud is Different
Every CNAPP has evolved past being a static checklist by now. The real gap is prioritization and evidence.
Most tools are still selling “panic as a service”: everything gets flagged, nothing gets triaged. Point tools that bolt AI monitoring onto existing stacks don’t solve this either, instead just adding one more enumerated asset class to the same undifferentiated pile.
| CNAPP | AI Security Add-On Tools | OX Cloud | |
| When it acts | Periodic/batch scans of posture and vulnerabilities | After deployment, bolted onto existing cloud tooling as an add-on | Continuous inventory; real-time detection on live infrastructure |
| What it covers | Posture, misconfigurations, vulnerabilities in infrastructure only | One AI asset class enumerated alongside existing coverage | CNAPP coverage, plus non-human identity and live AI/prompt visibility |
| Organizational context | Generic rules applied uniformly | Generic rules, bolted on, no environment-specific context | Evidence-linked to what’s actually reachable in your environment |
| Effect on backlog | Adds findings without reachability context so backlog grows | Adds another list of findings alongside existing tools | Structural noise reduction so unreachable findings fall away |
| Over time | Stays static between scan cycles | Stays static, treats AI as one more asset to enumerate | Feeds the same live evidence model as the rest of the OX platform |
Most vendors in this space sell AI governance as inventory: a list of AI assets, a list of models, a posture score. That answers “what do we have” and stops there. It’s the same answer whether your environment is doing something dangerous or nothing at all.
OX Cloud goes further: the CNAPP you expect, plus visibility into what an agent is actually doing.
What OX Cloud Does — Four Ways
IDENTIFY: Using Cloud Inventory you can see every workload, identity, and AI agent actually running in your cloud, not just what’s declared. Shadow AI and unmanaged non-human identities don’t stay hidden.
PRIORITIZE: Reachability decides what’s worth fixing. With Runtime Vulnerabilities and Attack Path Mapping features, misconfigurations, vulnerable packages, and supply-chain exposure that nothing can reach fall away. What’s left is reachable, evidenced, and fixable.

INVESTIGATE: Every alert opens into evidence, not just a finding with Cloud Graph and Runtime Events capabilities. You see who acted, what they touched, what else they could have reached. Graph-based investigation, not list-based triage.

GOVERN: Enforce the boundaries agents and code cannot cross with AIDR and Agentic Attack Surface capabilities. AI usage in production (agents calling tools, models accessing data, MCP servers executing) is monitored alongside conventional cloud workloads, in real time.

The Cloud Is Already Running Agents. Is Anything Watching Them?
Every CNAPP detects misconfigurations but they don’t truly tell you which ones an agent can actually reach.
What’s been missing is the ability to tell you what’s actually running, what it’s doing, and whether it matters before it becomes a headline.
That’s what OX Cloud is built for.
FAQ
What is CNAPP?
CNAPP stands for Cloud-Native Application Protection Platform, a category of tools that combines cloud posture management, workload protection, and vulnerability scanning into a single platform, rather than stitching together separate point tools for each.
A CNAPP typically covers configuration checks, container and Kubernetes security, and identity and access risk across cloud environments. Most CNAPPs today still run on a scan-and-flag model: they’re good at finding misconfigurations and vulnerabilities, but weaker at telling you which ones actually matter in your environment.
CNAPP vs. CSPM: what’s the difference?
CSPM (Cloud Security Posture Management) is one piece of what a CNAPP does. It specifically identifies misconfigurations and policy violations across your cloud accounts. A CNAPP is the broader platform: it typically includes CSPM alongside Kubernetes security (KSPM), data security posture (DSPM), workload and vulnerability scanning, and identity risk, unified under one platform.
In short, CSPM answers “is this resource configured securely?” while CNAPP is the umbrella covering posture, workloads, and runtime together.
Is OX Cloud a CNAPP?
Yes. OX Cloud provides the CNAPP coverage security teams expect: CSPM, KSPM, DSPM, compliance monitoring, and vulnerability visibility across hosts, containers, and cloud accounts.
But it doesn’t stop at posture. OX Cloud extends that same coverage into runtime and AI-specific visibility, watching non-human identities and AI agent activity as they actually operate in your environment, not just what’s configured. That’s the shift from inventory-and-posture to evidence of what’s actually happening.
How do I secure AI agents in the cloud?
Securing AI agents in the cloud starts with knowing they exist. Many non-human identities and AI agents operate with no clear owner and no visibility into what they can access. From there, it means monitoring what agents actually do in production: which tools they call, what data they touch, and what permissions they hold, in real time rather than on a scan cycle.
Reachability matters here too, filtering for what’s actually exploitable, rather than flagging every configuration as equally urgent, is what turns agent monitoring into something a team can act on.
What is shadow AI in the cloud?
Shadow AI in the cloud refers to AI models, agents, and tools running inside your cloud environment without security or IT’s knowledge or approval such as unauthorized MCP servers, unsanctioned integrations, or agents a team spun up without review.
Because cloud environments already sprawl across accounts and workloads, this activity tends to blend in, especially for tools built to check configuration rather than watch behavior. The real risk here is that no one’s tracking what it’s doing or accountable for the outcome.
What is AIDR?
AIDR (AI Detection and Response) is live detection and governance of AI-driven usage, configuration, and threats across cloud and runtime environments, in real time rather than on a batch or scan-cycle basis.
It’s built to catch what static posture tools miss: AI agents calling tools, models accessing data, and MCP servers executing on their own, as it happens.
What is runtime security?
Runtime security is visibility into what’s actually running in your environment right now (workloads, containers, and processes) rather than what’s declared in configuration or caught on a periodic scan. A vulnerability that’s live and reachable in production is a very different risk than the same vulnerability sitting dormant and unreachable.
Pairing runtime signals with posture findings is what lets a team tell the two apart instead of treating every finding the same.
What are non-human identities?
Non-human identities (NHIs) are the service accounts, API keys, AI agents, and automated processes that hold access and permissions in a cloud environment without a human directly behind each action. They tend to accumulate over time, often with no clear owner, broader permissions than they need, and no one accountable for what they can reach.
That makes them a distinct and growing risk category: an agent or service account can access data and take actions at machine speed, long after anyone remembers why it was granted access in the first place.