TL;DR
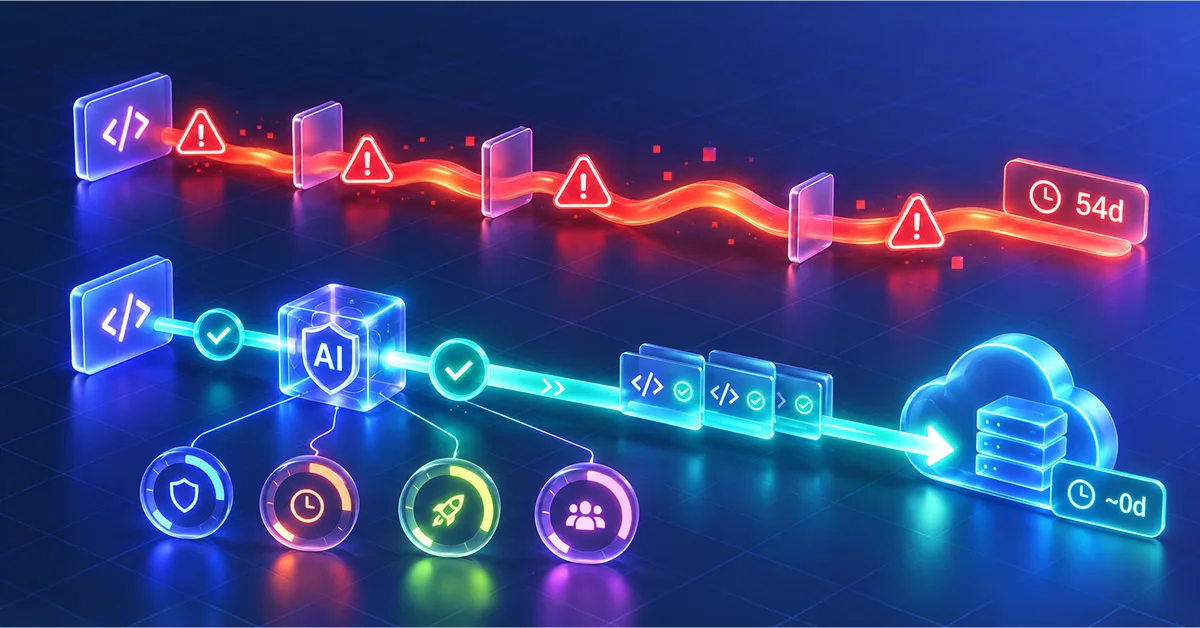
- Mean time to remediate (MTTR) is the average time from detecting a vulnerability to deploying and verifying its fix. For high and critical application and API vulnerabilities, the average MTTR in 2025 was 54.81 days. Early detection, clear ownership, documented processes, and automation shorten it. MTTR alone misleads; pair it with mean time to detect, recurrence rate, and Secure Velocity.
- Early detection, coverage, clear ownership, communication, and standardized, documented vulnerability management policies and processes help reduce MTTR. Automation and new AI tools greatly enhance the efficiency of vulnerability management workflows.
- MTTR is only one of many vulnerability management metrics. You should also assess mean time to detect (MTTD), validation time, patch compliance, remediation and recurrence rates, exploitability scores and recurrence risks, and other relevant metrics.
- Focusing on MTTR alone can be misleading and negatively impact security outcomes. Measuring Secure Velocity using the OX Security platform and factoring exposure across your software development lifecycle (SDLC) helps you more accurately communicate the success of your AppSec projects and identify where improvements can be made.
Why Mean Time to Remediate (MTTR) Vulnerabilities Must Be Measured
The mean time to remediate (MTTR) vulnerabilities in your IT infrastructure must be measured. This allows for continuous, demonstrable improvement, and allows security leaders to clearly communicate the importance and effectiveness of the work their AppSec technicians are performing to secure your organization.
This guide explains why you need to measure MTTR, and what you can do to actually reduce the time from detection to remediation by improving coverage, assigning ownership, clearly communicating threats and risks, documenting and standardizing, and utilizing your AppSec platform’s automation and AI features.
The Definition of MTTR Differs Based On What You’re Measuring
MTTR can have different meanings in AppSec, cybersecurity, and incident response based on context:
- Mean time to remediate: Mean time to remediate (MTTR) is the average time from when a vulnerability is detected to when its fix is deployed and verified.
- Mean time to restore/recover: The mean time taken for a system to return to normal operation after an incident.
- Mean time to respond: The average time from the first alert to recovery. This is not the same as mean time to acknowledge (MTTA), which is the time from the alert to when work begins.
Knowing which MTTR you are measuring is important: in vulnerability management, mean time to remediate is the primary metric. However, the time to remediate can be affected by the time to acknowledge a vulnerability, and it also affects the time it takes to recover if a vulnerability is exploited and a system is affected.
The MTTR calculation is simply the sum of the total remediation times, divided by the number of vulnerabilities. While this would ideally all be measured in minutes, in vulnerability management, MTTR is often measured in months, leaving exploitable weaknesses in your IT infrastructure.
For accurate MTTR calculations, you must thoroughly track each step of the application vulnerability management lifecycle, and keep a record of all open, remediated, and mitigated vulnerabilities.
What Does a “Good” MTTR Look Like?
In cybersecurity, ‘good’ doesn’t mean ‘good enough’; it should be a secure baseline for your specific infrastructure that meets your operational goals. Context, as always, is key, and must be maintained across security workflows so that measurements and targets have real meaning.
Generally speaking, however, critical vulnerabilities that are reachable should be remediated or mitigated within hours, and others within as short a time frame as possible. Mandiant’s M-Trends 2026 report puts the mean time to exploit vulnerabilities at an estimated -7 days, meaning exploitation routinely happens before a patch is released. The proliferation of AI-powered attacks will continue to accelerate this.
This can be impractical for small teams, making automation that identifies and reacts to new vulnerabilities 24/7 increasingly important. This is now essential with the increase in AI-powered attacks that are active around the clock, constantly probing internet-facing services and compromising supply chains.
Vulnerability prioritization also factors into the MTTR outcome, as remediating low-impact vulnerabilities may be put off for cost or technical reasons, or in favor of focusing on more exploitable vulnerabilities. While this is not ideal, operational concerns will be a factor.
In addition, the application security KPIs that you measure should reflect real-world exposure risks in your organization, rather than ad-hoc benchmarks that can drift. You should establish realistic targets and service-level objectives (SLOs) and ensure that they are met.
Why You Need to Measure and Reduce MTTR
MTTR will fluctuate as vulnerabilities are found and closed, and your systems, development tools, and software supply chain change. Your goal is to continually adapt to keep it as low as possible.
Measuring success identifies where you can improve and also gives you hard evidence you can take to stakeholders to prove that your efforts are informed and effective. MTTR also affects the service-level agreements (SLAs) that you enter with your customers. Even if you don’t directly provide software or services, every business stores sensitive information about their clients, staff, and users, and must take active measures to protect apps and data and alert affected parties if it is threatened.
Why Vulnerability Management Metrics Don’t Paint the Full Picture
While MTTR is important, relying on it as the sole indicator of the performance and effectiveness of your vulnerability management can be misleading. Focusing only on this metric may lead to prioritizing speed over effectiveness, giving a false sense of security, and missing real-world security and compliance goals.
Other important metrics to measure to improve and inform decision-making include:
| Vulnerability Management Metric | Meaning |
| Mean Time to Detect | How long it takes on average to discover a vulnerability |
| Validation Time | How long it takes to validate that a deployed fix is effective |
| Patch Coverage and Patch Time | The percentage of assets that are covered, and how long it takes for them to be patched. Cumulatively used to calculate the patch compliance rate |
| Detection Rate | The number of vulnerabilities being identified |
| Remediation Rate | The number of vulnerabilities being remediated |
| Recurrence Rate | How frequently vulnerabilities are re-introduced (e.g., via a system restore, or as part of an outdated container image) |
| Exploitability Score | Standardized scores for measuring how easily exploited a vulnerability is |
| Vulnerability Risk | This is a score unique to your organization that communicates the unique risk a vulnerability poses to your infrastructure, factoring severity, exposure, and reachability |
| Number of Open Vulnerabilities | The number of detected but unremediated vulnerabilities at a given time |
You should not:
- Change your testing conditions to artificially lower your MTTR (or any other metric/score). Ground your calculations and assessment in reality and real risk/impact.
- Assume that a drastic improvement after changing your vulnerability management tools or workflows is a good thing. Check that vulnerabilities aren’t being overlooked and that KPIs are being measured accurately.
- Use post-mortems to shift responsibility: they are there to make your next response faster and better.
With all metrics, keep context in mind. As your vulnerability management improves, you’ll start to catch more vulnerabilities, increasing the count and possibly skewing calculations or causing unnecessary alarm.
The Levers That Actually Reduce MTTR for Vulnerabilities
Reducing MTTR for software vulnerabilities should be done in stages, focusing on the easy wins first. Then, you can build policies, processes, and introduce your own risk assessments to ensure that your vulnerability management process directly addresses your environment and ensure that resources are efficiently assigned to further reduce MTTR.
Early Detection and Coverage
Tool choice is critical for early detection: continuous vulnerability management that covers your entire software development lifecycle (SDLC) and infrastructure must cover all assets and integrate with your tools. Vulnerabilities cannot be remediated if they are not known, and the sooner they are found the sooner they can be fixed.
OX Security, an AI-Native Application Protection Platform (AINAPP), integrates with your SDLC, providing full coverage and early detection at the first appearance of a vulnerability.
Ownership and Communication
Every vulnerability should have an ultimate owner, whether assigned by project, system, or other domain. Ownership may change as the vulnerability progresses through the vulnerability management lifecycle. Repeatable policies and processes, training, and drills for how to respond to an active vulnerability should be established so that when a vulnerability isn’t addressed by automated tools, it can be quickly remediated and verified.
Clear communication ensures context is maintained, risk is correctly assessed, and that remediation is confirmed. Involving stakeholders who understand the reachability of an exploit in your systems can help reduce noise and avoid false positives.
Documentation and Standardization
Policies and ownership should be documented to ensure that both the correct action, and who is responsible for it, is clear. Standardized processes communicated in runbooks make repeatable processes faster and reduce gaps and avoid human error that can result in re-work and affect MTTR.
Automation and AI
Automation is a necessity for vulnerability management. It is practically impossible for even a team of technicians to review every vulnerability in a modern software supply chain. AI takes this further with intelligent assessments that can assess the unique risk a vulnerability poses in your own environment, rather than relying on broad threat scores. AI can also suggest and implement mitigation and remediation measures, further reducing the gap between detection and remediation.
OX deploys AI-powered fixes within your workflow that address real risks, and save developers’ time with clear diffs and commit previews.
Alert Fatigue, Backlogs, and MTTR
Alarmingly, the MTTR for many organizations stretches to months. For high and critical severity application and API vulnerabilities, the average mean time to remediate in 2025 was 54.81 days. This is often caused by a backlog of low-priority or overlooked vulnerabilities, as alert noise from new vulnerabilities and ‘putting out fires’ often distracts from the backlog.
While these may be considered low-risk, they pose an ongoing, compounding threat. Reducing your MTTR for vulnerabilities gives you capacity to deal with outstanding risks, while ensuring that critical new vulnerabilities are resolved rather than added to your backlog.
Accurate triage helps solve alert fatigue, combining early detection with ownership and automation in a repeatable process. Rather than chasing false positives or prioritizing vulnerabilities that are actually unreachable, you can validate AI-suggested compensating controls and patches, and focus on critical vulnerabilities with real exploit paths.
Why Prevention at Creation Is the Ultimate MTTR Lever
An MTTR for vulnerabilities as close to zero as possible should be your goal. Detecting a vulnerability the moment it enters your supply chain actually brings this to zero.
Prevention at the time of creation, whether hand- or vibe-coded, makes this possible. By embedding security into the SDLC, rather than just downstream in CI/CD pipelines, vulnerabilities are detected in real-time, before they can be executed. An SBOM and context that spans development, testing, and deployment environments, allow real-world risk to be established, automated remediation tools to act instantly and appropriately, and the relevant stakeholder to be immediately notified.
OX VibeSec ensures you can realize the full benefit of AI coding tools, while recognizing and addressing the novel risks they introduce.
How to Communicate the Effectiveness of Your SDLC Security to the Board
The shorter your MTTR, the less time an attacker has to identify and exploit a vulnerability in your systems. However, MTTR on its own paints an incomplete picture. As a result, relying on it as your sole metric for decision-making can negatively impact security outcomes.
Communicating the cumulative impact of your MTTR and other vulnerability management metrics, and their meaning in context, can be challenging. Failure to do so can undersell the security investments your organization makes, or overstate their effectiveness, leading to a false sense of security.
Secure Velocity is an OX Security metric. It’s the rate at which your organization ships software that is safe at creation, expressed as the ratio of risk prevented before merge to the time exposed code stays reachable in production. Its four components are Prevention Rate, Exposure Window, Fix Velocity, and Agent Velocity. See how OX measures Secure Velocity.
FAQs
Mean time to remediate (MTTR) is the average time from when a vulnerability is detected to when its fix is deployed and verified.
MTTR can be reduced by improving detection with security tools that fit your use case and maintain context across the vulnerability management process. Clear communication and ownership will help reduce gaps, while automation enables a proactive security posture. Automated tools that correlate, deploy, and verify fixes, while generating evidence, also reduce MTTR.
A “good” MTTR is dependent on context; there is no universal benchmark. CISA’s Binding Operational Directive 22-01 gives US federal agencies two weeks to remediate known exploited vulnerabilities, and the 2025 industry average for high and critical application vulnerabilities was 54.81 days. Treat reachable, actively exploited criticals as same-day work and set service-level objectives for the rest.
MTTR is calculated by summing the total remediation times, and dividing that number by the number of vulnerabilities. This makes it important to carefully track every step of the vulnerability management cycle, and maintain a record of all open, remediated, and mitigated vulnerabilities.